
Open-source tools that turn offensive security evidence into defensive controls.


ExploitSpec turns a confirmed HTTP exploit into a deterministic, reviewable regression test. It keeps pentest evidence alive after remediation by proving three things:
- RED — the invariant fails on the known-vulnerable baseline;
- GREEN — it passes after the fix;
- STABLE — the fix keeps passing across repeated runs.
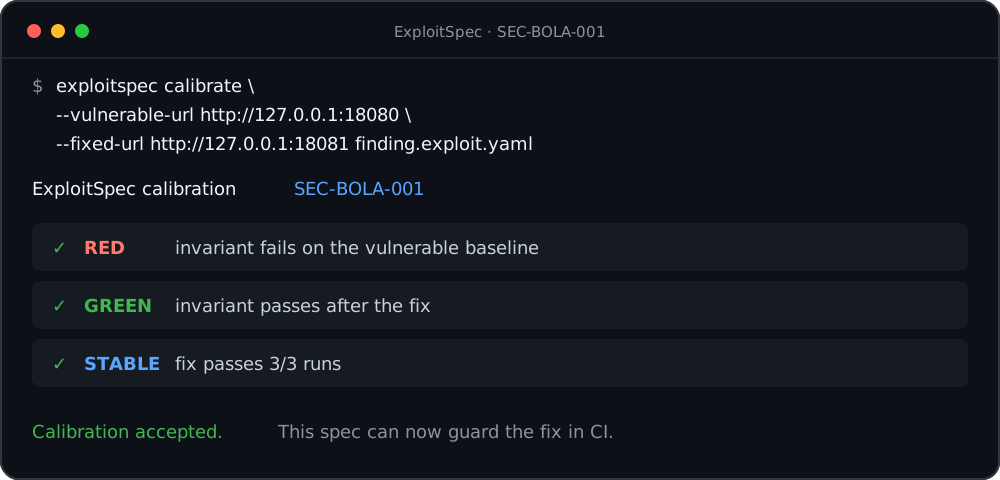
Try the complete synthetic demo locally:
git clone https://github.com/pazent/exploitspec.git
cd exploitspec
make demo
No account. No telemetry. No paid tier. Apache-2.0.
We care about narrow security promises, reproducible evidence, deterministic tests, conservative handling of secrets, and honest documentation of limits.
- Read the specification
- Install the GitHub Action
- Fork the passing consumer template
- Read the BOLA/IDOR case study
- See the roadmap
- Propose an idea
- Contribute
Maintained by Alessandro · GitHub.
