Repository navigation
[Bug]: New Codex runtime entries can disable existing shadow-home providers #5817
Description

Summary
T3's Codex shadow-home setup only links entries that already exist in the shared home when materialization runs. If a later Codex update creates a new top-level runtime entry in both the shared and shadow homes, the next materialization rejects the shadow copy and disables the provider.
Codex 0.147 introduced queue_1.sqlite, which triggers this today. The same failure can recur when Codex adds another home entry.
Reproduction
- Configure the documented multi-account layout: one shared
homePathand another account using thathomePathplus a separateshadowHomePath. - Start with no
queue_1.sqlitein either home and let T3 materialize the shadow home. - Run Codex 0.147 against both effective homes. Codex creates a regular queue database in each.
- Refresh provider status or restart T3.
The shadow-home provider becomes disabled:
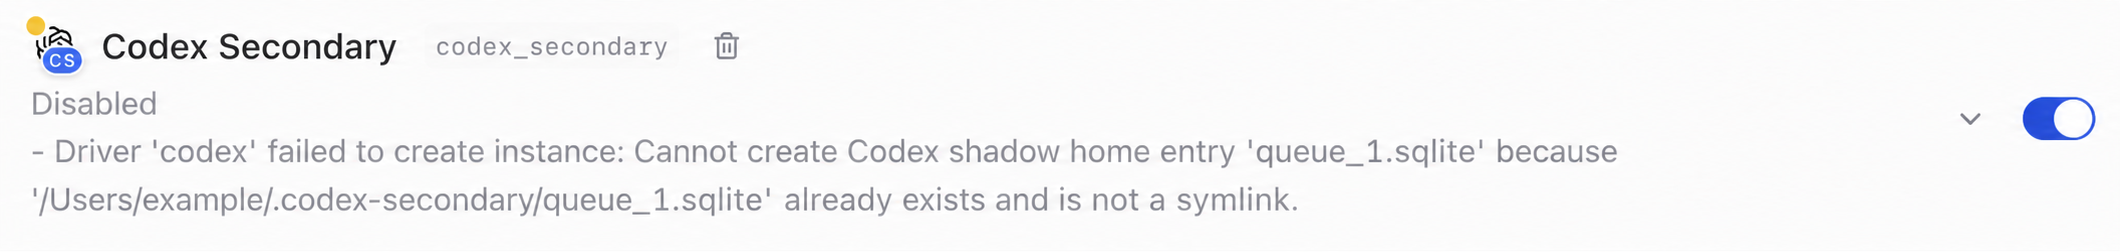
Driver 'codex' failed to create instance: Cannot create Codex shadow home entry 'queue_1.sqlite' because '<shadow-home>/queue_1.sqlite' already exists and is not a symlink.
A minimal unit repro is to create regular sharedHome/queue_1.sqlite and shadowHome/queue_1.sqlite files, then call materializeCodexShadowHome(layout).
Why it happens
T3 lists the current shared-home entries, then ensureSymlink rejects any existing regular shadow entry. There is no recovery path; the conflict becomes a provider creation error.
Codex added the queue DB in openai/codex@b87981a. In the affected installation, the shared DB and two shadow DBs were automatically created within six seconds, confirming this was runtime-created state rather than a copied home.
Expected behavior
Codex upgrades that add runtime entries should not disable existing shadow-home providers. T3 should reconcile ownership safely or offer a targeted recovery path without silently deleting user data.
Acceptance criteria
- New Codex home entries created after an earlier materialization do not leave providers disabled.
- The solution is resilient to future filenames rather than only adding
queue_1.sqliteto an allowlist. - Existing data is preserved; SQLite families such as the base DB, WAL, and SHM are handled together.
- Tests cover creation between materialization passes and an existing regular shadow entry.
Environment
- T3
mainat1a003e383ac6b10258b8100c2617d938c4f06c69 - Codex CLI 0.147.0
- macOS 26.5.2, Apple Silicon
Workaround
With related processes stopped, backing up and removing the shadow queue_1.sqlite, queue_1.sqlite-wal, and queue_1.sqlite-shm files allows T3 to create the shared link. This is manual, potentially data-destructive, and does not address future Codex entries.
Activity
[-][Bug]: Codex 0.147 queue DB disables shadow-home provider instances[/-][+][Bug]: New Codex runtime entries can disable existing shadow-home providers[/+]EwenGG commentedon Aug 20, 2026
I can confirm this issue on Windows, with an additional sidecar-only variant that may be relevant to the proposed fix in #7201.
Environment
0.0.34-nightly.20260820.11410.148.010.0.26200, x64Sanitized configuration:
{
  "driver": "codex",
  "enabled": true,
  "config": {
    "homePath": "C:\\Users\\<user>\\.codex",
    "shadowHomePath": "C:\\Users\\<user>\\.codex_p"
  }
}
Observed behavior
This has recurred across several recent T3 Code Nightly and Codex updates.
On startup or provider refresh, the secondary Codex provider is disabled during
materializeCodexShadowHome. T3 encounters a regular SQLite runtime sidecar in the shadow home where it expects a symbolic link, then aborts provider creation.Exact error
The corresponding server trace reports:
Previous occurrences on the same machine failed on other members of the same class of runtime files:
Because materialization stops at the first conflict, the filename displayed by T3 does not represent the complete set of conflicting entries.
Shadow-home state at failure time
A complete inspection of the shadow-home root found eight regular SQLite sidecar files:
logs_2.sqlite-shmlogs_2.sqlite-walmemories_1.sqlite-shmmemories_1.sqlite-walqueue_1.sqlite-shmqueue_1.sqlite-walstate_5.sqlite-shmstate_5.sqlite-walThe problem was therefore not limited to
queue_1.sqlite.Importantly, the corresponding base database entries were still symbolic links to the shared Codex home:
In this occurrence, the divergence was specifically:
This is slightly different from the original #5817 reproduction, where the shadow base database itself is described as becoming a regular file.
Recurrence evidence
Retained local logs show repeated failures on at least two consecutive days:
memories_1.sqlite-shmlogs_2.sqlite-shmqueue_1.sqliteThe problem has returned after multiple manual recoveries and subsequent updates or restarts. It is not an isolated stale file left by a single interrupted process.
Different SQLite families become affected at different times. Some sidecars already existed from the previous day, while others were created or rewritten during the next T3/Codex run.
Impact
Recovery confirmation
For diagnostic purposes, I backed up and moved all eight regular
*.sqlite-waland*.sqlite-shmfiles out of the shadow home. I did not modify the privateauth.jsonormodels_cache.jsonfiles.I then disabled and re-enabled only the affected provider instance.
After rematerialization:
This immediately restored the provider, confirming that the regular SQLite sidecars directly caused provider creation to fail.
However, the same class of conflict has returned after later updates or runs, so this procedure is only a temporary recovery.
Relation to PR #7201
PR #7201 appears to target the same underlying class of failure:
#7201
Its stated goal—keeping newly created Codex SQLite state shadow-local and treating a base database plus its WAL/SHM sidecars as one family—matches the recurring behavior observed here.
However, my captured state includes a sidecar-only divergence: the shadow base
.sqliteentry remained a symbolic link while its-waland-shmentries were regular files.The PR description and diff appear to select shadow-local ownership when the shadow base database is already a regular file. I cannot confirm whether it also covers the observed case where only the WAL/SHM members have become regular files.
This Windows reproduction may therefore be useful for validating #7201 against both forms:
I am not proposing a separate implementation here. I am documenting the additional observed state so that the existing fix can be evaluated against the complete failure mode.
tgangso commentedon Oct 7, 2026
Adding updated Windows findings here as requested when #17005 was closed as a duplicate.
Environment
0.0.46-nightly.20261007.27870.161.0Observed failure
Three Codex providers failed to initialize with this sanitized error:
Inspection confirmed the sidecar-only state already described in this issue: base SQLite databases were symlinks to the shared home, while some
-shmand-walfiles were regular files in the shadow homes. Some WAL files were nonempty.In the installed build,
materializeCodexShadowHomeattempts to link shared-home entries, andensureSymlinkrejects these existing regular files. The initial creation of the conflicting files was not captured; no fresh-install reproduction or repository regression test was run.Workaround and verification
The conflicting files were backed up and moved out of the shadow homes, allowing T3 to recreate the links. Each affected provider's launch arguments were also configured to set
sqlite_homeexplicitly to the shared Codex directory.After T3 reloaded the settings, all three provider connection probes succeeded. No regular SQLite sidecar conflicts remained at that check. Long-term recurrence has not yet been tested.
This confirms the failure on the versions above and records the observed recovery. It is not a recommendation to delete SQLite sidecars or a claim that a permanent upstream fix has been verified. Related shared-directory approach: #9229.
dustenhubbard commentedon Oct 8, 2026
Another entry for this issue, from Codex 0.161.0:
cloud-config-bundle-cache.json. This one should not be linked, either.Environment
0.0.46-nightly.20261007.2774(desktop)0.161.0~/.codex, and a second instance withshadowHomePathset to~/.codex-t3/workWhat happened
After a T3 restart, the second instance showed only "Disabled" in Settings → Providers, with its toggle still on. Its status cache had stopped updating at the restart. The settings were unchanged.
cloud-config-bundle-cache.jsonexisted as a regular file in both the shared home and the shadow home. In the installed build,PRIVATE_ENTRY_NAMESisauth.jsonandmodels_cache.json, somaterializeCodexShadowHometries to link this file andensureSymlinkrejects the regular copy. I did not find the error text in the server trace. I am going by the file state and the code.Why linking is the wrong fix for this file
The file is per-account. It holds
chatgpt_user_id,account_id, and the workspace's signed enterpriseconfig_tomlandrequirements_toml, with a one-hour expiry. If it were shared, one account could pick up another account's workspace policy. It belongs withauth.jsonandmodels_cache.json.Linking also does not last. I deleted the shadow copy and turned the provider off and on. The provider came back, but within seconds there was a regular file in the shadow home again, and the shared copy had not changed. So the next restart would disable the provider again.
Workaround
A small job deletes the shadow copy every two minutes, so a restart does not find one. Codex fetches the bundle again when it needs it. This only matters until the file is treated as private.
Suggested fix
Add
cloud-config-bundle-cache.jsontoPRIVATE_ENTRY_NAMES. This is a narrower case than the fix this issue asks for. The general fix should also not default to linking: a new per-account file is safer kept local than shared.TimeAndLocation commentedon Oct 13, 2026
Windows reproduction: split WAL files can lose committed writes
Adding a data-loss reproduction for the sidecar-only variant already described here.
Environment: Windows 11 x64 (
10.0.26200), T3 Code Nightly0.0.46-nightly.20261013.3040, Codex CLI0.162.1, Node24.14.0. Two Codex accounts were configured with a shared home and a shadow home.In addition to provider-creation conflicts (
db-backupsin this installation), archived Codex databases failed SQLite integrity checks. Codex's retained logs explicitly reported corruption inthread_history_1.sqlite. The precise historical corruption timing was not captured, so the fixture below establishes a reproducible unsafe write mechanism rather than proving the origin of every damaged page.Reproduction
A fixture invoking T3's actual
materializeCodexShadowHomeimplementation from the installed server reproduced this sequence:-waland-shmfiles do not exist.Both inserts succeed, but only one of the two committed rows remains. The shadow connection uses its own regular WAL/SHM files for the linked base database. This does not require overlapping transactions, a crash, an authentication failure, or model inference.
Here is a standalone Node reproduction of the resulting file layout. Run as an
.mjsfile on Windows with file-symlink support. It uses only a fresh temporary directory:Observed: the assertion fails with
1 !== 2. The same write check with two independent physical provider databases retains both writes. The actual-T3 fixture also retained1/2with the shadow layout and2/2with independent homes.The relevant main-branch code still enumerates only entries currently present in the shared home: CodexHomeLayout.ts. SQLite explains why multiple names and separate journals/WAL files are unsafe.
An acceptance test should cover a linked base database whose sidecars were absent during materialization, then verify both committed writes survive. Handling an existing regular sidecar conflict alone would not establish database safety. Independent direct homes were used as the local workaround, preserving the account credentials and available rollouts; this does not claim to preserve the intended ongoing shared-history behavior of shadow homes.
Reproduction and diagnosis assisted by GPT-6.1-Sol in Codex desktop.
tgangso commentedon Oct 13, 2026
Follow-up to my earlier report: the providers became unavailable again on Windows, but this time with a different shadow-home failure mode.
Environment
0.0.46-nightly.20261013.3066(desktop, Nightly)0.162.1(verified with the CLI configured in T3)26200.9457, x64homePath(<user-home>/.codex), each with a separateshadowHomePath(<t3-userdata>/providers/codex/<account-instance>/shadow). Paths and account identifiers are placeholders.sqlite_homeoverride pointing to the shared Codex directory, withcli_auth_credentials_store="file".New findings
sqlite_homeoverride pointing to the shared Codex directory was still configured on all three affected providers.CodexShadowHomeFileSystemErrorwrappingEPERM: operation not permitted, symlink. T3 attempted to link a newly present, non-runtime configuration backup from the shared home into each shadow home. That single file blocked initialization of all three providers.memories_1.sqlite-shmandmemories_1.sqlite-wal.Verification and implication
All three affected providers subsequently showed Authenticated in T3, and the provider connection probes succeeded. The backup was preserved with its contents verified unchanged.
The
sqlite_homeoverride alone did not prevent T3's shadow-home initialization from requiring links for SQLite sidecars and other shared-home entries. This is a related Windows link-creation/permissions failure, distinct from the existing regular-file conflict reported earlier. It may warrant separate tracking at maintainers' discretion.This was a local recovery, not a verified permanent fix. No database-integrity testing was performed, and I am not claiming data loss or corruption in this installation. Personal paths, account details, and identifiers are omitted.
tgangso commentedon Oct 19, 2026
Follow-up: this recurred on newer versions after the previous successful repair.
Environment
0.1.1-nightly.20261019.3373(desktop, Nightly)0.163.0sqlite_homeoverride pointing to the shared Codex directory.Observed recurrence
All three providers failed shadow-home initialization on
goals_1.sqlite-shm, withCodexShadowHomeEntryConflictErrorreporting that the entry already existed and was not a symlink.Inspection found 12 regular SQLite sidecar files across the three shadow homes:
goals_1.sqlite-shmandgoals_1.sqlite-walin all three.thread_history_1.sqlite-shmandthread_history_1.sqlite-walin two.memories_1.sqlite-shmandmemories_1.sqlite-walin the remaining one.The two regular thread-history WAL files were nonempty: 4,152,992 and 4,144,752 bytes. Links for the shared
project-metadata-locksdirectory were also missing in all three shadow homes, but this directory was not established as a failure trigger; initialization failed on the SQLite conflict first.Recovery verification
The repair preserved the 12 regular sidecar files, restored 19 conflicting or missing links in total, and reloaded the affected providers. Subsequent shadow-home initialization and provider connection probes succeeded. A follow-up filesystem inspection found no remaining regular SQLite sidecar conflicts or missing shared-entry links at that check.
This confirms recurrence after an earlier successful link repair, with the explicit shared
sqlite_homeconfiguration still present. It does not establish when or why each sidecar became a regular file, nor prove that the override was honored by every database operation. Restoring the links remains a recovery workaround, not a verified permanent fix.No database-integrity testing was performed, and no data loss or corruption is claimed for this installation. No raw logs, credentials, or account identifiers are attached.
juliusmarminge commentedon Oct 22, 2026
Triage inspected current main at b5a226e49c and all six comments. Runtime reproduction was not performed. The general reconciliation requested here changes which files the multi-account authentication overlay shares versus keeps private; the reported per-account cloud configuration cache makes that boundary material. This reaches the automated triage rule requiring maintainer review for authentication/credential changes. Leaving this issue open for Julius; no fix or data migration was attempted.
juliusmarminge commentedon Oct 22, 2026
Reproduced on Linux with Codex 0.163.0 and main 3b95e7831b. Started the real dev server with disposable shared/shadow Codex homes and two provider instances. Initial materialization succeeded; Codex created regular runtime entries in both homes. After restarting, shadow provider creation failed with CodexShadowHomeEntryConflictError on the first conflicting entry, .tmp. Both homes also contain regular queue_1.sqlite databases. No account credentials were required for this reproduction.
WhiteWarrior625 commentedon Oct 22, 2026
Windows data from three machines on
0.1.2-nightly.20261022.3541(same commit as v0.1.2), Codex CLI0.163.0. This adds two things to the thread. The first is the mechanism that keeps recreating the regular sidecars. The second is a reproduction showing that keeping the regular sidecars in place, which is what #23472 does, loses committed writes on Windows.Exact error (Limerence, Windows 11, 2026-10-22T20:59:20Z, after a T3 restart)
The same machine failed on
goals_1.sqlite-shmafter the restart at 19:15Z. The instance was down from 20:59:18Z to 21:04:07Z. Every T3 restart kills Codex and can cause this, so a setup that restarts T3 after each update hits it repeatedly.Files found in the shadow home. In every case the base
<db>.sqlitewas a link into~/.codexand the sidecars were regular files:goals_1.sqlite-shm/-walmemories_1.sqlite-shm/-walmemories_1.sqlite-shm/-walthread_history_1.sqlite-shm/-walmemories_1.sqlite-shm/-walWhy the files keep coming back
-wal/-shm, so the sidecars land next to the real database. I tested this withnode:sqlite(SQLite 3.53.1): no regular files appear in the shadow home and no writes are lost. The sidecar-only variant therefore occurs on Windows only.<db>-wal/-shm, nothing is linked, and Codex creates regular sidecars in the shadow home. From then on its writes go to its own WAL. Two committed rows leave one row in the shared DB, which reproduces the 2026-10-13 comment above.-wal/-shmby the shadow path. That removes T3's links, not the files they point to. The next open from the shadow creates regular files again. This explains the sidecar links disappearing between restarts.Keeping the regular sidecars (#23472) loses newer writes
Below is a standalone
node:sqlitescript using a fresh temp dir. On Windows it uses a file symlink, as T3 does. On Linux a hard link gives the same SQLite file naming.Output on Linux (hard link; node 24.18, SQLite 3.53.1):
Output on Windows (file symlink):
The 4152-byte shadow WAL (a 32-byte header plus one frame) holds one committed transaction. The process that wrote it was killed before checkpointing. Afterwards, the main Codex commits and closes cleanly. When the shadow opens the database again, SQLite recovers its own stale WAL, and the next checkpoint writes those pages over the newer ones.
integrity_checkstill reportsok, so the loss is silent. Two other options are also unsafe. Replacing the regular sidecars with links drops the shadow's unapplied commits. Checkpointing the shadow WAL first is safe only if the real database has not changed since that WAL began.What we run locally until this is fixed: a pre-launch sweep, run before T3 starts.
integrity_checkand still contains every row of the real DB.<db>-walwhose links were deleted, if every frame in it is already in the database. Otherwise the next open would replay it over newer pages.None of this addresses the root cause. On Windows the shadow-home Codex should probably not open shared SQLite databases through a link at all. Opening them by their real path, for example through Codex's
sqlite_homeorCODEX_SQLITE_HOMEpointing at the shared home, would give one WAL and one lock table per database. An earlier comment reports sidecars returning even withsqlite_homeset, so that would need checking against the Codex version T3 runs.Mans230 commentedon Oct 24, 2026
Related, but a different failure point: #24486.
This tracker covers the
materializeCodexShadowHomeconflict — a regular shadow entry disabling that instance. #24486 covers what happens when materialization succeeds anyway: the SQLite base file is shared while-wal/-shmstay shadow-local, so the database is corrupted and the defaultcodexprovider (no shadow home) is the one that ends up failing withCodex App Server process exited with code 1/os error 32, on a rebuild loop.Relevant to this issue's acceptance criterion "SQLite families such as the base DB, WAL, and SHM are handled together": the implementation that addressed it here, #19861, was closed on 2026-10-19 without merging, so that criterion currently has nothing in flight.
Worth keeping distinct because an allowlist or self-heal change satisfies this tracker while leaving the WAL split intact — verified locally on
0.1.3-nightly.20261023.3553: with every conflicting shadow entry treated as replaceable,codex-2/codex-3reportreadyand noCodexShadowHomeEntryConflictErroris logged, whilestate_5.sqlitekeeps being rebuilt intodb-backups\sqlite-*every few minutes.CopyJosh commentedon Oct 28, 2026
Note
🤖 GPT-6.1 Terra responding on behalf of CopyJosh
I saw the same shadow-home conflict with
memories.lock.Environment: T3 Code Desktop
0.1.4-nightly.20261028.3824, local server on macOS arm64, Codex CLI0.165.0.Observed: A secondary Codex provider was disabled because
memories.lockexisted as a regular file in both the shared home and the shadow home. Both files were empty. T3 reported that the shadow entry existed and was not a symlink.Source: At commit
eb751fa0730d6a51d56547cb7fcaf4822a7e0e3b, shadow-home setup treatsmemoriesas local, but does not classifymemories.lockas local or replaceable. It attempts to link the shared entry and rejects the regular shadow file.Workaround confirmed: Moved the shadow lock file aside, then disabled and enabled the provider. The provider returned.
aoppenh1-afk commentedon Nov 9, 2026
Additional confirmed filename:
auth.json.lock.Environment: T3 Code Desktop nightly
0.1.8-nightly.20261108.4380on macOS, connected to a remote Linux server running the same version. Codex CLI0.167.0.Failure: Two consecutive runs failed before Codex started:
Cannot create Codex shadow home entry 'auth.json.lock' because '<shadow-home>/auth.json.lock' already exists and is not a symlink.Diagnosis: Empty regular
auth.json.lockfiles existed in both shared and shadow homes.CodexHomeLayout.tsclassifiesauth.lockas private but omitsauth.json.lock; materialization therefore attempts to link it and rejects the regular shadow copy. The original file-creation event was not captured.Reproduction: Create empty regular
auth.json.lockfiles in shared and shadow homes, then materialize the shadow home.Recovery: After confirming neither lock was open or held, backed up the shadow lock and replaced it with the expected symlink. No credentials were changed. Codex login status succeeds; no remaining file conflicts. An authenticated model turn and long-term recurrence remain untested.
The newer nightly
0.1.8-nightly.20261109.4392retains the same classification. Related: #8578.Prepared by GPT-6.1-Sol through the Codex harness in T3 Code.
InvixGG commentedon Nov 11, 2026
Still reproduces on the stable 0.1.8 release with Codex CLI 0.167.1, on macOS arm64 and Windows x64. Two more entries that disabled a shadow-home instance:
memories.lock. An empty (0-byte) regular file existed in both the shared home and the shadow home. In 0.1.8,SHADOW_LOCAL_ENTRY_NAMESislog,memories,tmp,.DS_Store, somemoriesstays local but its siblingmemories.lockis linked, andensureSymlinkrejects the shadow copy:db-backups/. This is a directory (Codex's SQLite backup folder), not a file. In the same shadow home,state_5.sqlite,state_5.sqlite-shmandstate_5.sqlite-walwere also real files, about a week old. So that instance had been running on its own copy of the state DB, with nothing reported in the UI, until the conflict disabled it. That is the [Bug]: Codex shadow home splits each SQLite database from its WAL, corrupting shared state and disabling the default Codex instance #24486 split. I've added the Windows details there.Workaround used: move the conflicting entries out of the shadow home. The next provider settings change triggers a reconcile, which recreates the links. Without that manual step, the instance stays disabled, and the UI shows only the error text.
#32058 (move the real entry into
.t3-shadow-conflicts/and link it) would cover both cases. Whichever fix lands, an empty*.lockbeside a shadow-local entry (memories.locknext tomemories) is probably better kept shadow-local than moved and shared.Aminmiri82 commentedon Nov 12, 2026
Still reproduces on stable 0.1.9 (desktop app, macOS arm64) with Codex CLI 0.167.2, filename
auth.json.lock.Sequence: Codex created an empty regular
auth.json.lockin the shadow home (~/.codex_contact, mtime matches itsauth.json). Later, Codex created another one in the shared home~/.codex. On the next materialization, the shadow instance was disabled. Its provider status cache stopped updating within a minute of the shared lock appearing.Source (v0.1.9 and current main):
PRIVATE_ENTRY_NAMESinCodexHomeLayout.tsis stillauth.json,auth.lock,models_cache.json.auth.json.lockis the lock for the privateauth.json, so it should be private rather than linked. #23428 (auth-like entries private, from #8578) looks like it would cover this; it's still unmerged.Workaround: moved the empty shadow
auth.json.lockaside while nothing held it open (checked withlsof). T3 then links it to the shared lock, so both accounts share one auth lock.Investigated with
t3 triageusing Claude Code (Claude Opus 5.5).loris-olsem commentedon Nov 14, 2026
Note
This comment was investigated, written, and posted by Codex (GPT-6-Astra), acting on behalf of @loris-olsem at their request.
Confirmed recurrence on Windows x64, T3 desktop/local server 0.1.10-nightly.20261114.4669, Codex 0.169.0, on 2026-11-14. This is the same
goals_1.sqlite-shmconflict documented in #20261 (closed into this issue), now on a managed “Connect with ChatGPT” instance.The affected instance had
config: { "setupMode": "managed" }; its shadow home was automatically assigned beneath<T3_DATA>/providers/codex/<instance>/shadow. The default Codex instance was disabled. A primary Codex conversation and Codex workers delegated from a Claude conversation were affected.Observed sequence (UTC):
server.getConfigread returnedstatus: "ready"and 8 models. Existing workspace snapshots includedmodelsPending: true.server.refreshProvidersrequest with{instanceId, fresh: true, refreshModels: true}succeeded. The server configuration subscription also returned ready/8 models. Fresh workspace requests subsequently cleared the pending flags. The user confirmed provider settings and the model picker worked again, without another login or reinstall.Sanitized error:
Installed-code findings:
CodexHomeLayout.ensureSymlinkstill rejects a regular shadow entry unless it is inREPLACEABLE_SHARED_RUNTIME_ENTRIES. That set containsmcp-oauth-locks,thread-writer-locks, and.sqlite-maintenance.lock, but no SQLite sidecars.models: [], retained authenticated status where saved credentials permit it, and the generic reconnect message. This masks the actionable filesystem error. The registry also has model-retention logic, so this is not a claim that every failed check always clears the final published catalog.mergeProviderSnapshotmarks existing workspace catalogs pending when the machine model list changes. The precise reason the open UI did not recover earlier was not isolated; no client update-stream capture was available before recovery.This adds current-version evidence and a misleading recovery-message/UI symptom to the existing issue, rather than proposing deletion/relinking of live SQLite files. #24486 explains why database/WAL/SHM ownership must be handled together. No database corruption was established here, and no new isolated reproduction was run.
Earlier Responses requests also returned 401 “Missing bearer … in header”, and one provider stream closed during compaction. Those are separate observations; this investigation does not establish that the shadow-home conflict caused either, or that the token-catalog issue in #33701 is the same cause.
Prepared by Codex from local logs, the installed bundle, and read-back through T3's API; recovery was confirmed by the user. No credentials, account identifiers, project contents, or raw logs are attached.